Infinet

Flat-style illustration of a healthcare clinic workstation with overlapping interface panels on screen, suggesting shared access and system ambiguity—visually supporting the concept of hidden IT risks in clinics with shared devices.

Hidden IT Risks in Clinics with Shared Devices

Most clinics don’t operate in quiet, controlled office environments.

In community clinics and multi-provider practices, front desks stay busy, exam rooms turn over quickly, and staff move between systems all day long. Workstations are shared across shifts. Devices are logged into, stepped away from, and picked back up—often within minutes.

In that kind of environment, technology isn’t just supporting care—it’s woven directly into the pace of operations.

That’s also where many IT risks in clinics quietly take hold.

Not because teams are careless, but because clinical workflows prioritize speed, access, and continuity of care.

And when systems are designed like traditional offices instead of real clinics, clinic cybersecurity risks tend to surface in ways leadership doesn’t see until there’s a problem.

Why Clinics Face a Different Category of IT Risk

Healthcare IT environments operate under constraints most businesses don’t.

You’re balancing:

Limited downtime tolerance

Patient experience

Clinical efficiency

Compliance requirements
Healthcare team working across connected systems with patient data, lab tools, and digital records, illustrating how everyday workflows can introduce IT risks in clinics when systems and visibility aren’t fully aligned.

Unlike a single-user office setup, clinics rely on shared devices healthcare environments—front desk computers, exam room workstations, tablets, printers, and specialty systems that multiple people touch every day.

Federal healthcare guidance has long recognized shared workstations as a risk area when access controls and session management aren’t aligned with real workflows.

From an IT perspective, that changes everything.

Risk isn’t just about firewalls or antivirus software. It’s about how systems behave when:

  • Logins are reused
  • Sessions stay open
  • Devices move between rooms
  • Accountability becomes blurred

These conditions don’t look dangerous on paper. But operationally, they create gaps that traditional “check-the-box” security doesn’t address.

Shared Devices: Convenience That Quietly Expands Exposure

Shared workstations are common in clinics—for good reason. They keep workflows moving.
Clinic staff using shared systems and patient records across a digital healthcare workspace, illustrating how shared devices can contribute to IT risks in clinics when access and accountability are not clearly managed.

But from a risk standpoint, shared devices introduce challenges that are easy to underestimate:

Inconsistent access control
Staff roles change, but permissions don’t always follow at the same pace.

Unclear user accountability
When multiple staff use the same device, it’s harder to trace actions back to individuals—especially during audits or investigations.

Session overlap
A user steps away without logging out. Another steps in. Patient data remains accessible longer than intended.

This is one of the most overlooked IT risks in clinics—not because leaders don’t care, but because the risk is embedded in everyday efficiency.

Good security controls for shared workstations doesn’t fight this reality. It adapts to it.

The Front Desk: Where Workflow Speed Meets Data Sensitivity

It doesn’t come as a surprise that the front desk is one of the busiest—and most exposed—areas in any clinic.

It’s where:

  • Patient data is first accessed
  • Payments are processed
  • Appointments are scheduled
  • Phones, printers, and systems converge

From a cybersecurity standpoint, this creates a dense intersection of systems, people, and sensitive information.

Common front-desk risks include:

  • Screens visible to patients or visitors
  • Credentials shared across shifts
  • Devices left unlocked during high-traffic moments

None of this signals negligence. It signals operational pressure.

The real issue is that clinic cybersecurity risks here are environmental, not technical. And operational risk in healthcare environments require intentional design—not just security software.

Fast Workflows Create “Invisible” Risk Accumulation

Speed is essential in healthcare. But speed also compresses margin for error.

When workflows move fast:

  • Security steps get bypassed unintentionally
  • Policies exist but aren’t practical
  • Training fades under real-world pressure

Over time, small exceptions become the norm. And risk quietly accumulates, warranting intentional IT planning.

This is why many clinics feel “mostly secure” until something forces a closer look—an audit, a breach, a vendor requirement, or an insurance question.

At that point, leaders aren’t asking:

“What tools do we need?”

They’re asking:

“Where are we actually exposed?”

What “Good” Looks Like in a Shared-Device Clinic Environment

Mature protection in clinics doesn’t mean locking everything down or slowing care.

It means designing systems around how clinics actually operate.

That includes:

  • Role-based access that matches real workflows
  • Clear session management on shared devices
  • Visibility into who accessed what—and when
  • Training that reflects reality, not policy documents

Most importantly, it means leadership-level clarity around system access and accountability.

When protection is intentional, clinic leaders can confidently answer:

  • Are we managing risk—or just reacting to it?
  • Do our workflows align with compliance expectations?
  • Could we explain our security posture if asked tomorrow?

That confidence doesn’t come from more tools. It comes from alignment.

How InfiNet Approaches Clinic IT Risk (Without Disrupting Care)

At InfiNet, our role isn’t to introduce complexity or fear.

It’s to help clinic leadership:

  • See where risk actually lives
  • Understand tradeoffs clearly
  • Make decisions that fit clinical reality

That means working from workflows outward—not from tools inward.

When clinics understand their exposure, they’re able to protect patients, staff, and operations without sacrificing efficiency or trust.

Start With Clarity

If you’re unsure where risk actually exists in your clinic—or whether your current setup reflects how your team truly works—start with visibility.

A clear, practical assessment from a local managed IT provider can help you understand exposure without disrupting care or overcorrecting.
Professional woman using a tablet in a modern office with InfiNet branding and “Get in touch with our team” text.

Frequently Asked Questions

1. What are the most common IT risks in clinics?

The most common IT risks in clinics come from shared devices, unclear access controls, fast workflows, and limited visibility into user activity—not from lack of technology.

2. Why are shared devices risky in healthcare?

Shared devices healthcare environments make accountability and session control harder, increasing the chance of unauthorized access or data exposure.

3. Are clinic cybersecurity risks different from other industries?

Yes. Clinics prioritize speed, access, and patient care, which creates unique operational risks that standard office security models don’t fully address.

4. How can clinics improve security without slowing workflows?

By aligning access controls, session management, and training with real-world workflows instead of rigid policies that don’t reflect daily operations.

5. Is cybersecurity mainly an IT responsibility in clinics?

No. While IT plays a key role, clinic cybersecurity risks affect leadership, compliance, operations, and patient trust—making it a shared responsibility.

Hidden IT Risks in Clinics with Shared Devices Read More »
Flat illustration of an IT professional reviewing systems on a planning board, representing an IT reset for businesses through structured evaluation and oversight.

New Year IT Reset for Businesses: Setting the Year Up Right

January has a way of exposing things you managed to live with all year.

Budgets reset. Projects resurface. Leadership asks new questions. And suddenly, the technology decisions you made incrementally—one tool here, one fix there—are sitting under a brighter light.

For many organizations, this is when an IT reset for businesses turns into a checklist exercise: patch systems, review backups, renew licenses, move on.

But the businesses that start the year strongest don’t treat January as a technical cleanup.
They treat it as a strategic IT reset.

A reset shouldn’t just involve asking, “Is everything working?”—but instead, “Is our technology truly aligned with the business’s goals for this year?”

That distinction matters—because misaligned IT doesn’t usually fail loudly. It quietly creates risk, waste, and friction that compounds long before anyone notices.

Why an IT Reset Matters for Businesses in January

January is one of the few moments when IT strategy for business can be made proactively, not reactively.

You have:

  • A clear view of last year’s breakdowns and near-misses
  • Fresh financial context
  • Leadership attention before the year accelerates

Handled correctly, an IT reset for businesses lets you:

  • Reduce meaningful risk early in Q1
  • Reclaim wasted spend before it compounds
  • Align systems to real business outcomes—not assumptions

Handled poorly, January becomes a rushed audit that checks boxes without changing trajectory.

The difference isn’t effort.
It’s how you frame the work.

January is one of the few moments where technology decisions can be made proactively, not reactively.

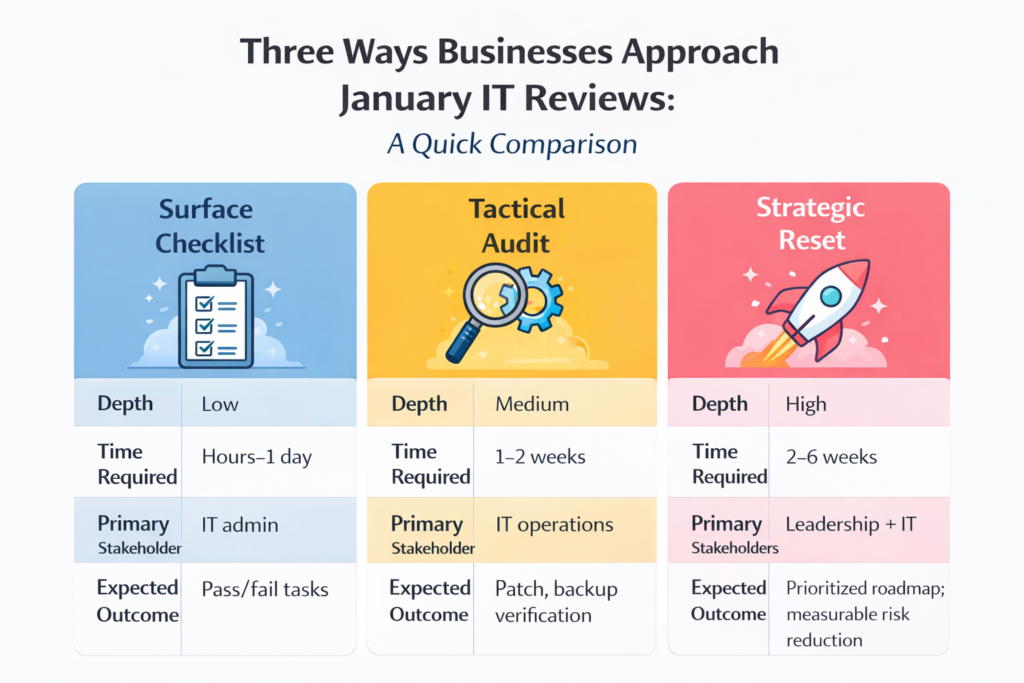
A Quick Comparison: Three Ways Businesses Approach January IT Reviews

Comparison graphic titled “Three Ways Businesses Approach January IT Reviews” showing Surface Checklist (low depth, quick pass/fail tasks), Tactical Audit (medium depth, patch and backup verification), and Strategic Reset (high depth, leadership-driven roadmap and measurable risk reduction), illustrating an IT Reset for businesses.

Most businesses operate in the middle by default.

The organizations that mature fastest intentionally move up the stack—not by doing more, but by deciding better.

A Practical New Year IT Reset: What to Review (and How to Go Deeper)

Below isn’t a list of tools.
It’s a set of decision areas that determine whether IT supports or silently undermines the business.

Align Technology to the Business Plan

Start by identifying your top three business priorities for the year.

Then map:

  • Which systems support each priority
  • Required performance expectations (SLAs, uptime, response)
  • What failure would cost the business

If a system doesn’t map to a priority, it raises a hard but necessary question:
Why are we funding this?

This is where many organizations uncover shadow spend and legacy tools that survived without justification.

Treat Backups as Recoverability Projects

Backups often give leaders a false sense of security.

Most businesses assume that if data is being backed up, it can be restored quickly when something goes wrong. In reality, many organizations don’t discover gaps until they’re already under pressure—during a ransomware event, a system failure, or an accidental deletion that disrupts operations.

The real question isn’t whether backups exist.
It’s whether your business can actually recover fast enough to avoid downtime, lost revenue, or operational chaos.

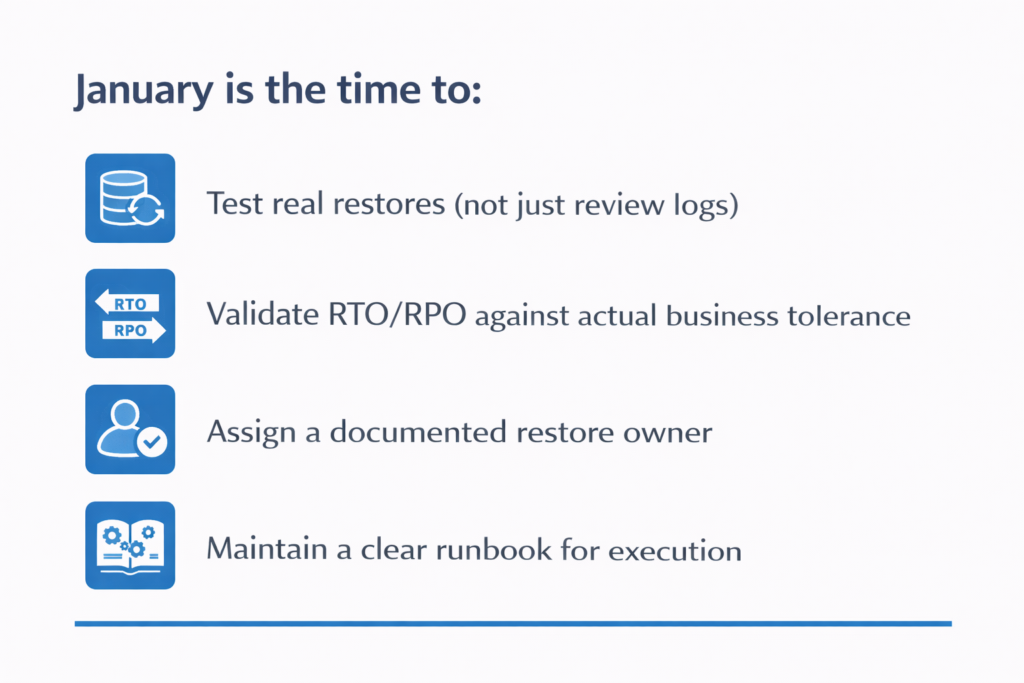
That’s why January is the right time to treat backups as a recoverability exercise, not a checkbox.

Calm, structured checklist graphic outlining four January IT Reset for businesses tasks: testing real restores, validating RTO/RPO, assigning a restore owner, and maintaining a clear runbook. Minimal blue icons appear beside each item in a clean, systems‑oriented layout.

The question isn’t “Do we have backups?”
It’s “Can we recover fast enough to avoid real damage?”

Move from Vulnerability Lists to Attack-Path Reduction

Scanning tools generate noise. Attackers exploit pathways.

A stronger January reset focuses on:

  • Identity and privileged access
  • Exposed services
  • Lateral movement opportunities

Breaking attacker chains reduces risk more effectively than chasing every CVE.

This shift requires context, prioritization, and leadership buy-in—not just alerts.

Rationalize SaaS and Licensing Spend

Most organizations underestimate how much budget disappears into unused or overlapping subscriptions.

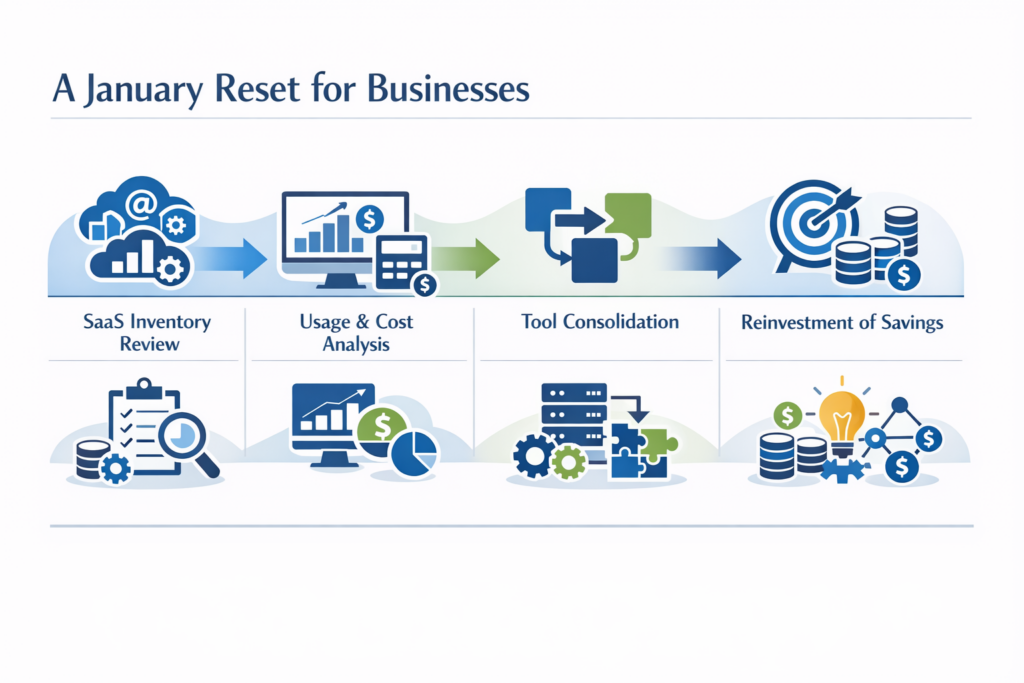
A January reset should include:

  • Full inventory of SaaS tools
  • Usage vs. cost analysis
  • Consolidation where it reduces complexity
  • Intentional reinvestment of savings
Structured horizontal process graphic illustrating four components of an IT Reset for businesses: SaaS inventory review, usage and cost analysis, tool consolidation, and reinvestment of savings. Uses calm tech-focused icons, restrained blues and greens, and a systematic left‑to‑right flow consistent with InfiNet’s brand aesthetic.

This is often where businesses fund higher-impact security or automation—without increasing total spend.

Rebuild Observability and Runbooks

Alerts without action create fatigue.

Effective systems ensure:

  • Every alert maps to a documented response
  • Clear ownership and escalation paths
  • Tabletop exercises for the top two incident types

When something breaks, the goal isn’t speed alone—it’s clarity under pressure.

Review Vendor and Contract Health

January is the safest time to examine:

  • SLA performance
  • Renewal timelines
  • Exit clauses
  • Vendor risk concentration

Consolidation only makes sense when it reduces risk and friction—not when it’s driven by convenience.

Address People and Skills Gaps

Technology maturity stalls without the right human support.

Rather than trying to fix everything, identify:

  • One critical skills gap
  • One short-term training or advisory investment
  • One clear owner for cross-team coordination

Progress beats perfection—especially early in the year.

What “Good” Looks Like Coming Out of January

By the end of a true IT reset, leadership should be able to answer:

  • Where does our biggest risk actually live?
  • Which systems matter most—and why?
  • What are we intentionally not fixing yet?
  • Who owns the next 90 days?

If those answers are clear, the year starts on stable footing.

If they’re vague, the organization is already behind.

Frequently Asked Questions

1. What is an IT reset?

An IT reset is a structured review of systems, risk, and spend that aligns technology decisions to business goals—rather than a simple technical checklist.

2. Why is January the best time to review IT?

January offers fresh budgets, leadership focus, and the opportunity to reduce Q1 risk before issues compound later in the year.

3. How is an IT reset different from an IT audit?

Audits confirm compliance and configuration. An IT reset prioritizes outcomes, tradeoffs, and forward-looking decisions.

4. Do small businesses need a strategic IT reset?

Yes—often more than larger organizations. Smaller teams feel the impact of outages, waste, and misalignment faster and more directly.

5. What role does a vCIO play in an IT reset?

A vCIO provides leadership-level guidance, translating technical findings into business decisions and building a prioritized roadmap.

6. How long should a proper IT reset take?

Typically 2–6 weeks, depending on complexity. The value comes from clarity and prioritization—not speed alone.

A Thoughtful Next Step

If January already feels busy, that’s exactly why clarity matters.

A short, focused conversation can help you understand:

  • Where risk is underestimated
  • Where spend is misaligned
  • What a realistic 90-day plan looks like

That’s how strong years begin. Here’s to a clear, intentional start.

Professional man seated and using a tablet with office background, featuring InfiNet logo and contact message.

New Year IT Reset for Businesses: Setting the Year Up Right Read More »

Flat illustration of a calm, modern IT planning workspace with a central monitor showing layered system blocks, a desk calendar indicating future timelines, and subtle icons representing AI, cloud services, and data backup. Muted colors and clean lines emphasize structure, readiness, and forward-looking planning.

2026 IT Planning for Omaha Businesses: What Matters Most

As 2025 winds down, many Omaha small and mid-sized businesses are already looking ahead to 2026 IT planning for Omaha businesses—especially when it comes to budgeting, infrastructure, and long-term technology decisions.

And they should.

The pace of change has shifted from “fast” to “blink and suddenly you’re navigating new cybersecurity requirements, rising costs, and more operational complexity than expected.”

Cyber Insurance Isn’t Optional — And Requirements Are Getting Tougher

Carriers aren’t playing anymore.

Expect 2026 policies to require:

  • Mandatory MFA across all apps
  • EDR (think SentinelOne, Huntress, etc.)
  • Encrypted backups
  • Documented incident response plans
  • Proof that you actually test your backups

If you can’t check these boxes, you’ll either pay more… or be denied.

Omaha SMBs should get ahead of this now while the requirements are still manageable.

Illustration of multi-factor authentication on a mobile device, representing cybersecurity planning and identity security for 2026 IT planning for Omaha businesses.
Illustration representing written policies and documentation, supporting AI governance and planning in 2026 IT planning for Omaha businesses.

AI Tools Are Becoming Practical — But Also Risky

By 2026, AI won’t be “cool extra functionality.”
It’ll be baked into everything:

  • email triage
  • ticket deflection
  • quality control
  • meeting summarization
  • client communication
  • data analytics

But here’s the twist: the more AI you use, the more data governance and security of AI-connected apps matter.

Businesses should start setting policies NOW for:

  • what data AI tools can access
  • what tools are allowed
  • where proprietary files can (and cannot) go
  • how vendors handle retention

Your staff WILL adopt AI — with or without permission.
Better to make a plan before chaos unfolds.

Illustration representing written policies and documentation, supporting AI governance and planning in 2026 IT planning for Omaha businesses.
Cloud computing illustration representing Microsoft 365 services, storage, and increasing cloud costs.

Microsoft 365 & Cloud Costs Are Going Up

Not a scare tactic — a trend.

Across 2024–2025, Microsoft, Google, and most SaaS vendors introduced global price increases tied to:

  • added security tooling
  • increased storage
  • currency adjustments
  • bundled AI features

2026 will almost certainly continue that movement.

To prepare:

  • Audit who actually needs which license
  • Remove stale accounts
  • Adjust sharing/storage policies
  • Clean up unused services
  • Budget for cloud cost optimization
Illustration showing review of cloud services and licenses for cost optimization.
Visual symbolizing Azure Active Directory and cloud identity supporting hybrid work environments.

The Traditional Office Network Is Changing

By 2026, hybrid work will be the norm — even among Omaha businesses.

That means:

  • fewer on-prem servers
  • more cloud identity (Azure AD)
  • better VPN replacement tools
  • device management (Intune)
  • stronger remote monitoring

Businesses should plan for an environment where any employee, on any device, from any location still has to meet the same security standards.

This requires a different IT architecture than 2018.

Backup & Disaster Recovery Needs to Be Faster

For 2026, we’re recommending businesses move toward:

  • immutable backups
  • cloud-to-cloud replication
  • tested recovery timelines
  • documented failover plans
  • offsite + in-tenant redundancy

If your last backup test was “we think it’s fine,” 2026 will not be kind to you.

Cloud backup and disaster recovery illustration showing data replication across devices.
Role-based access control illustration representing identity and access management.

Businesses should prioritize:

  • passwordless options
  • strong MFA
  • conditional access rules
  • SSO consolidation
  • role-based access reviews
  • employee offboarding workflows

Your firewall matters.
Your identity architecture matters more.

Legacy Line-of-Business Apps Will Become a Liability

If you’re running something old, unsupported, or duct-taped onto Windows 11 “hoping it holds,” 2026 is the year that breaks you.

Vendors are aggressively sunsetting:

  • old databases
  • old client-server apps
  • outdated accounting systems
  • unsupported medical, real estate, or manufacturing software

Plan ahead so you’re not scrambling when updates are no longer optional.

Flat, muted illustration of a vintage desktop computer with a CRT monitor and base unit, shown front-on with a blank screen, representing legacy systems or outdated technology.

2026 Belongs to the Businesses Who Prepare Now

The companies that thrive in Omaha next year won’t be the ones with the fanciest tools —
they’ll be the ones with a clear plan, secure systems, and technology that actually supports their operations.

If you want help building a 2026 IT strategy — cybersecurity, cloud, Microsoft 365, backups, AI policy, budgeting — we’re here for you.

Flat-style digital illustration of an IT professional using a tablet in a calm, modern office. In the background, multiple workstations display structured system dashboards. Text reads: “Get in touch with our team.” InfiNet logo shown.

2026 IT Planning for Omaha Businesses: What Matters Most Read More »

Semi-flat illustration of a business professional viewed from behind, seated at a desk and using a laptop, with simple abstract icons representing cookies connecting within a website interface, conveying how cookies support normal website functionality in a calm, trustworthy way.

The Sweet and the Sneaky Side of Cookies

Website cookies or simply “cookies”—named after the early computing term “magic cookie,” used to describe small pieces of data passed between systems—are small text files stored on your device when you visit a site. They help websites remember basic information, such as login status, preferences, or items left in a cart, so pages work as expected when you move around or return later.

Most of the time, cookies are simply part of how modern websites function. Problems arise when it’s unclear what’s being collected or why.

Cookies That Support Everyday Use: The “Good” Kind

Many cookies are essential to a smooth browsing experience. These are typically first-party cookies created by the site you’re actively using.

Common examples include:

  • Session cookies that keep you logged in as you navigate a site
  • Persistent cookies that recognize returning visitors
  • Preference cookies that remember settings like language or region

These cookies support usability and consistency. They’re designed to make sites work—not to monitor behavior across the internet.

Cookies Used for Tracking: The “Crumbly” Kind

Other cookies are designed to track activity beyond a single website. These are often third-party cookies used by advertisers or analytics platforms.

They collect information about browsing habits across multiple sites to build user profiles. That’s why a product you looked at once can seem to follow you from page to page afterward.

While tracking cookies aren’t automatically harmful, they do raise legitimate privacy concerns—especially when users aren’t aware of how much data is being collected or how it’s used.

4 Simple Ways to Manage Cookies

You don’t need to eliminate cookies entirely to improve privacy. A few small habits can make a meaningful difference:

  1. Review cookie settings instead of automatically accepting all options.
  2. Limit or block third-party cookies in your browser.
  3. Clear cookies and cached data periodically.
  4. Keep browsers and security tools up to date.

For businesses, cookie handling and data privacy should also be part of a broader security and compliance conversation—not an afterthought.

The Bottom Line

Cookies play a role in how the web works today. Some are necessary, some are optional, and some deserve closer scrutiny.

Understanding the difference helps you make informed choices—about your own browsing and about how your organization handles data. Clarity, not fear, is what leads to better decisions.

Flat-style digital illustration of an IT professional using a tablet in a calm, modern office. In the background, multiple workstations display structured system dashboards. Text reads: “Get in touch with our team.” InfiNet logo shown.

The Sweet and the Sneaky Side of Cookies Read More »

Thankful for Tech: How IT Keeps Omaha Businesses Running Smoothly

(And Why So Many Rely on InfiNet Solutions — Omaha’s Leading MSP)

As the year winds down, we all start thinking about what we’re grateful for: family, good food, and the tiny miracle that everything in the office keeps running even when half the staff is out for the holidays.

Here in Omaha, technology powers nearly every business — and as one of the region’s most trusted Managed Service Providers, InfiNet Solutions sees firsthand how crucial reliable IT really is. From cybersecurity to cloud services to automation, these tools keep organizations productive, protected, and moving forward every single day.

Let’s shine a little gratitude on the tech that holds it all together.

The Networks That Keep Omaha Working

Behind every smooth operation is an IT backbone built to handle real-world pressure.
When employees log in and everything “just works,” that’s the result of intentional engineering — the kind InfiNet delivers across Omaha and the Midwest.

Reliable networks aren’t luck. They’re architecture, monitoring, and proactive care.

Cybersecurity: Omaha’s First Line of Defense

Cyber threats don’t take holidays off, and neither do we.

With advanced tools like EDR, MFA enforcement, phishing protection, and real-time monitoring, InfiNet keeps companies in Omaha and beyond shielded from attacks long before they reach the network.

You won’t always see what gets blocked — that’s the point.
But you’ll feel the stability it brings.

Cloud Systems That Keep Teams Connected

Hybrid work, remote meetings, file collaboration — none of it happens smoothly without well-designed cloud architecture.

From Microsoft 365 to VoIP to secure remote access, InfiNet helps Omaha businesses stay connected anywhere, anytime. Consistency, speed, and security aren’t luxuries; they’re the new standard.

Backups & Business Continuity: Omaha’s Safety Net

Mistakes happen. Power goes out. Hardware fails.

But companies supported by InfiNet Solutions don’t panic — not when they know their systems are backed by robust, redundant, tested recovery strategies. When downtime could cost thousands, reliable backups aren’t optional. They’re essential.

Automation That Keeps Workflows Moving Without the Busywork

Smart automation has become one of the biggest productivity boosts for Omaha businesses, and it’s an area where InfiNet truly leads. From PTO approval flows, auto-scanning, and cross-department workflows, we build systems that quietly eliminate the manual tasks that drain time and cause delays. The result? Faster processes, fewer bottlenecks, and teams that spend more time on meaningful work instead of busywork. When technology works for you, everything runs smoother — and that’s exactly what we design it to do.

The People Behind the Tech

Technology is powerful, but expertise is what makes it thrive.

InfiNet’s team is known in Omaha for their approachability, deep technical knowledge, and forward-thinking solutions. Our clients trust us because we don’t just solve problems — we prevent them.

We build environments that grow with your business.
We guide leaders through complex decisions.
And we stay ahead of trends so our partners don’t fall behind them.

Tech keeps Omaha running — and we’re proud to be the team so many organizations count on to keep that tech reliable, secure, and seamless.

This season, we’re thankful for the tools that empower our community, for the businesses that trust us, and for the opportunity to serve as Omaha’s leading Managed Services Provider.

From all of us at InfiNet Solutions, Happy Thanksgiving — and here’s to another year of staying secure, productive, and confidently ahead of the curve.

Thankful for Tech: How IT Keeps Omaha Businesses Running Smoothly Read More »

Talk to our Team